Thales High Speed Encryptors protect data in motion across data centers, campus networks, and cloud connections at speeds from 10 Mbps to 100 Gbps - with near-zero latency and 2x bandwidth efficiency over legacy protocols like IPsec.
Thales Transport Independent Mode (TIM) allows encryption at Layer 2, Layer 3, and Layer 4 simultaneously - providing network-independent data protection that works across any infrastructure without protocol constraints.
Near-zero latency at full line speed
HSEs operate at the physical speed of the network with near-zero latency and no packet loss - independently certified by Miercom as delivering superior performance compared to IPsec.
2x bandwidth efficiency over IPsec
Unlike IPsec which increases packet overhead through tunneling, Thales HSEs use a thin encryption layer that preserves bandwidth and reduces the cost per protected gigabit by approximately 42%.
Hardware and virtual deployment
Available as physical appliances (1 to 100 Gbps, single to multiport) and as virtual encryptors for cloud and SDN environments - with a single management platform across both deployment types.
Post-quantum ready
Thales HSEs support Post-Quantum Cryptography (PQC) algorithms and Quantum Key Distribution (QKD) integration - future-proofing your network encryption investment against quantum computing threats.
Highest government certifications
Certified FIPS 140-3 Level 3, Common Criteria (EAL4+), NATO, and DoDIN APL (formerly UC APL) - used by defense agencies, governments, and critical infrastructure operators in over 35 countries.
Why Dedicated Encryption Beats Built-In IPsec
Most routers and firewalls already do IPsec, so the question buyers ask is fair: why add a dedicated encryptor at all? Two reasons - one about performance, one about who controls the keys. The diagram below shows the performance argument: the same Ethernet frame, encrypted two different ways.
Same original Ethernet frame, two different encryption pipelines - the IPsec tunnel overhead runs on shared router/firewall CPU capacity, while the HSE thin header runs on a dedicated encryption ASIC.
Backed by Independent Testing
+31.6%
Higher throughput than firewall-based IPsec encryption - Miercom 2024 independent test of the Thales CN6140
-48%
Less jitter when encryption is offloaded from the firewall to a dedicated HSE - Miercom 2024 independent test
-42.2%
Lower cost per protected gigabit vs. upgrading firewall encryption capacity - Miercom 2024 independent test
Thales HSE Product Lines
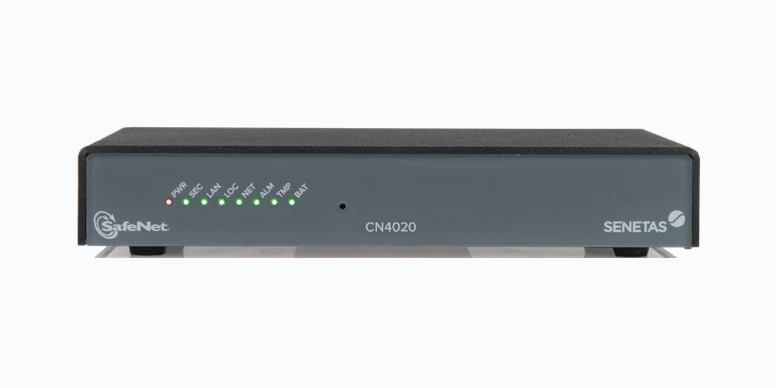
CN4000 Series
The entry point into Thales's High Speed Encryption line, built for branch offices and remote sites where a compact footprint matters as much as security. It handles speeds from 10 Mbps up to 1 Gbps over electrical (CN4010) or optical (CN4020) Ethernet, in a small-form-factor chassis that fits in a wiring closet rather than a data center rack.
Despite the entry-level positioning, it carries the same FIPS 140-3 Level 3 validation and Transport Independent Mode encryption as the rest of the CN-series - branch-office traffic gets the same assurance level as your data center, not a scaled-down version of it.
10 Mbps - 1 Gbps (electrical or optical Ethernet)
FIPS 140-3 Level 3 validated hardware
Compact, small-form-factor chassis
Best for: Branch offices, remote sites, and smaller locations that need data-center-grade encryption without data-center-grade hardware.
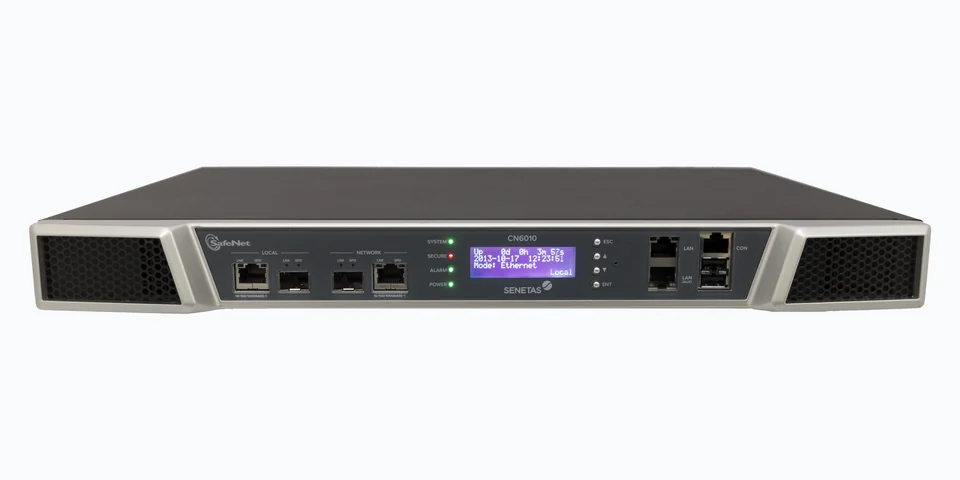
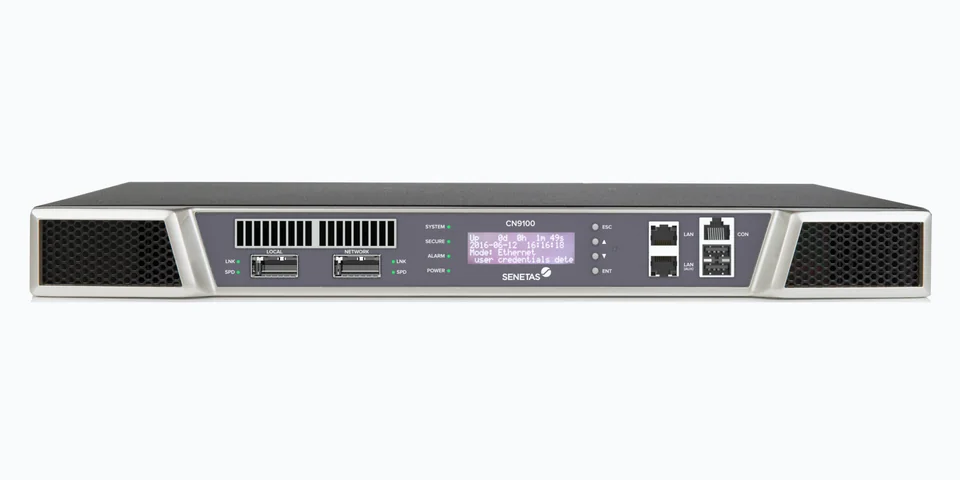
Thales's business-class encryptor line, scaling from 100 Mbps up to 40 Gbps with the CN6140's 4x10 Gbps multilink configuration. Built for private network links between offices, data centers, and colocation facilities where bandwidth needs grow over time.
Variable-speed licensing means the same hardware can be licensed up as traffic grows, without a forklift upgrade - and in Miercom's independent 2024 testing, the CN6140 delivered 31.6% higher throughput than firewall-based IPsec encryption at comparable link speeds.
100 Mbps - 40 Gbps (CN6140: 4x10 Gbps multilink)
FIPS 140-3 Level 3 validated hardware
Variable-speed licensing - scale without new hardware
Best for: Mid-size to large organizations connecting offices, data centers, or colocation sites over dedicated or carrier Ethernet links.
The high-speed end of the line, built for data center interconnects and core network links where every microsecond of latency has a cost. The CN9120 encrypts at up to 100 Gbps multipoint with under 2 microseconds of added latency - independently verified as among the lowest in its class.
At this speed, the difference between a dedicated encryption ASIC and a router or firewall's general-purpose CPU stops being marginal - it's the difference between a link that keeps up with 100G traffic and one that becomes the bottleneck.
Up to 100 Gbps, multipoint encryption
<2 microsecond added latency
FIPS 140-3 Level 3 validated hardware
Best for: Data center interconnects, core network links, and high-frequency or latency-sensitive traffic at 40-100 Gbps.
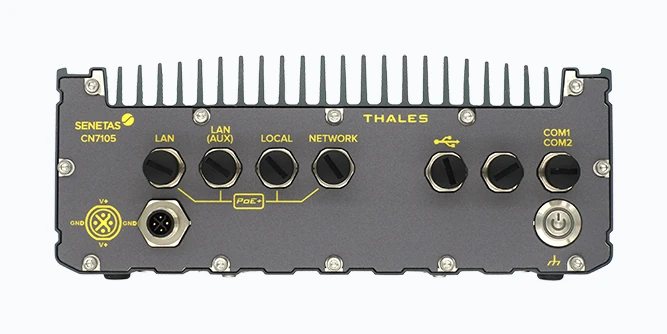
A ruggedized line built for environments no standard rack-mount encryptor survives: the CN7105 is IP67-sealed for outdoor deployment, the CN7107 is MIL-STD-810G tested for in-vehicle use, and the CN7108 is a compact, fanless option for IoT and edge locations.
Same Transport Independent Mode encryption as the rest of the CN-series, in enclosures built for vibration, temperature extremes, and dust and moisture exposure that would take a data-center-grade appliance out of service.
MIL-STD-810G tested; CN7105 is IP67-sealed
Outdoor, in-vehicle, and compact edge/IoT variants
Same Transport Independent Mode encryption as rack-mount CN-series
Best for: Defense, critical infrastructure, transportation, and industrial or outdoor sites where standard rack-mount hardware isn't an option.
A software encryptor for links where deploying physical hardware isn't practical - extended WANs, SD-WAN overlays, and cloud or virtualized network environments. It delivers policy-based, multi-layer encryption at up to 5 Gbps as a virtual network function (VNF), managed through the same platform as the hardware CN-series.
Because it's software, it deploys and scales the way the rest of your SD-WAN does - spun up on demand at a new site rather than shipped, racked, and cabled.
Up to 5 Gbps, policy-based multi-layer encryption
Deploys as a virtual network function (VNF)
Managed from the same platform as hardware encryptors
Best for: SD-WAN overlays, extended WAN links, and cloud or virtualized environments where hardware deployment isn't practical.
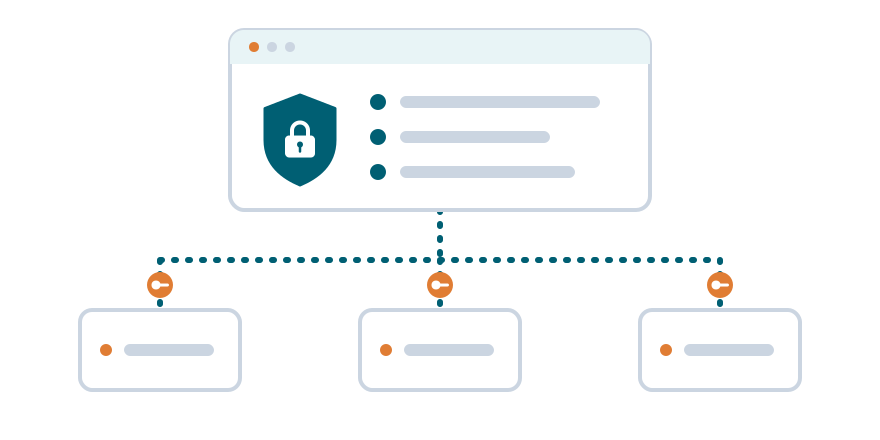
The reason HSE can be managed independently of your network team: Security Management Center (SMC) is a web-based platform for larger, multi-site deployments, with built-in PKI so it doesn't need separate certificate infrastructure. Encryptor Manager CM7 covers the same ground for smaller deployments.
Both can act as a Certificate Authority for your encryptors and give a security or compliance team full control over keys, certificates, and policy across every CN-series and CV1000 device on the network - without needing router or firewall administrator access.
SMC: web-based, built-in PKI, for larger/multi-site deployments
CM7: lighter-weight element manager for smaller deployments
Centralized key, certificate, and policy management, independent of network administration
Best for: Any HSE deployment where encryption keys and policy need to be controlled by security or compliance teams, separately from network operations.
Network traffic is exactly what 'harvest now, decrypt later' attacks target - data in motion captured today can be stored and decrypted once quantum computers make today's algorithms breakable. Thales HSEs already support post-quantum algorithms and Quantum Key Distribution (QKD) integration, so protecting network links today doesn't mean a forklift replacement when the migration deadline arrives.
Who Should Hold the Keys? The Case for Separating Network and Encryption Control
Router and firewall-based IPsec is configured and operated by the same network engineering team that manages routing, switching, and firewall rules - which means the team with day-to-day access to the network also holds the keys protecting the data crossing it. That concentration of control cuts against the separation-of-duties principle behind frameworks like PCI DSS and NIST's key-management guidance (SP 800-57): the people who can reach a system generally shouldn't be the same people who control the encryption protecting it, so that no single team - and no single compromised account - can both reach the data and unlock it.
Thales HSEs are managed independently of the network team, through Security Management Center or CM7, giving a security or compliance team direct control over encryption keys and policy without needing router or firewall administrator access - and giving network engineers full control of routing and switching without also holding the keys to the data crossing their network. In Thales's own customer research, 66% of security buyers rated separation of duties as an important or very important factor when evaluating a network encryption solution, so this isn't just a theoretical concern - it's something Thales customers are actively selecting for.
Frequently Asked Questions
IPsec is 15-25 years old and was not designed for modern network environments including SDN, 5G, and high-speed data center interconnects. Thales HSE provides 2x bandwidth efficiency over IPsec, near-zero latency, Layer 2/3/4 independence, and is designed for speeds up to 100 Gbps - where IPsec performance degrades significantly. HSE also provides stronger key management with FIPS 140-3 Level 3 certified hardware.
Thales HSE appliances support network speeds from 10 Mbps up to 100 Gbps (multipoint). The product range covers single-port and multi-port configurations, with virtual HSE options available for cloud and SDN environments. Contact us for the current product range and specifications.
Thales HSE is used by financial institutions (data center interconnects, SWIFT connections), telecoms (5G backhaul encryption), governments and defense (classified network encryption, NATO-certified), healthcare (patient data protection in transit), and critical infrastructure operators. Any organization that transmits sensitive data between sites or to the cloud is a potential use case.
Yes - Thales HSE is vendor agnostic and compatible with networking equipment from Cisco, Juniper, Nokia, Huawei, and other major vendors. The Transport Independent Mode removes protocol dependency, making HSE compatible with virtually any network infrastructure.
That's exactly the concentration of control that security best practice recommends avoiding. Frameworks like PCI DSS and NIST's key-management guidance (SP 800-57) favor separation of duties, so the team with day-to-day network access isn't also the sole holder of the encryption keys protecting the data on that network. Thales HSEs are configured and managed separately from routers and firewalls, through Security Management Center or CM7, so a security or compliance team can control keys and policy independently of network operations. In Thales's own customer research, 66% of respondents rated this separation as an important or very important factor when evaluating a network encryption solution.
Through two purpose-built platforms, separate from your router or firewall management tools: Security Management Center (SMC), a web-based platform with built-in PKI for larger and multi-site deployments, and Encryptor Manager CM7, a lighter-weight element manager for smaller deployments. Both let a security team configure, monitor, and rotate encryption keys and policy across every CN-series and CV1000 device, independently of whoever manages routing and firewall rules.
Get in touch
Request Thales HSE Pricing and Information
Tell us about your network encryption requirements - we will come back with a tailored proposal within one business day. As a Latvia-based Thales reseller, Sersor also provides local procurement, deployment support, and first-line support in your timezone.
Thank you!
Your request has been submitted. We will be in touch within one business day.