Thales Luna HSMs are the world leading hardware security modules for cryptographic key protection - FIPS 140-3 Level 3 certified, Common Criteria EAL 4+ certified, and trusted by governments, financial institutions, and enterprises worldwide.
Generate, store, and manage cryptographic keys in tamper-resistant hardware - ensuring keys never exist in plaintext outside the HSM boundary.
Public Key Infrastructure (PKI)
Protect certificate authority private keys and sign certificates with hardware-backed assurance - the foundation of secure PKI deployments.
Code signing
Sign software, firmware, and documents with cryptographic keys protected in certified hardware - meeting Microsoft, Apple, and other platform signing requirements.
Cloud and hybrid HSM deployment
Available as on-premises network HSM (Luna Network HSM), PCIe HSM (Luna PCIe HSM), and cloud HSM service - with hybrid configurations that combine local and cloud key storage.
Post-quantum crypto agility
Luna HSMs support post-quantum cryptographic algorithms and are designed to be crypto-agile - allowing organizations to migrate to new algorithms as standards evolve without replacing hardware.
High performance cryptography
Hardware-accelerated cryptographic operations deliver high throughput for applications with demanding performance requirements - from TLS acceleration to bulk encryption.
Luna General Purpose HSM Product Lines
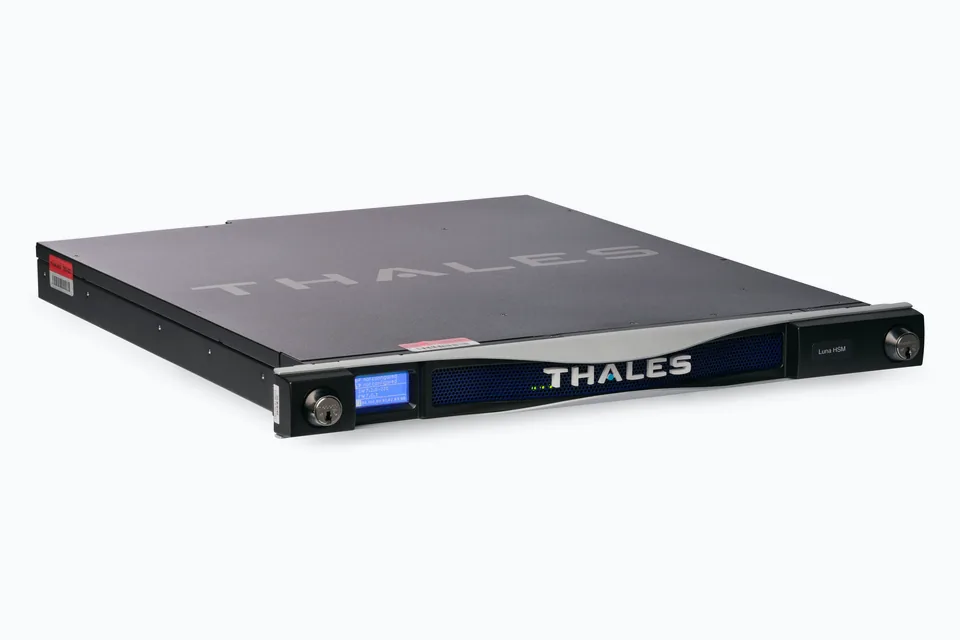
Luna Network HSM (Luna 8)
The flagship of the Luna line - a rack-mounted, network-attached HSM for enterprise and data center environments where many applications need shared, centralized access to cryptographic operations.
The current Luna 8 generation adds post-quantum cryptography support (ML-KEM, ML-DSA) alongside traditional RSA, ECC, and AES, and scales from the entry Luna 100 configuration up to Luna 190, so you size the appliance to the workload instead of over- or under-buying. Existing Luna 7 Network HSM deployments remain fully supported if you are not ready to move to the newest generation yet.
1U rack-mounted appliance with dual hot-swap power supplies
Three configurations (Luna 100 to Luna 190), up to 30 HSM instances per appliance
FIPS 140-3 Level 3 validated, eIDAS Qualified Signature/Seal Creation Device
Post-quantum ready (ML-KEM, ML-DSA)
Best for: Enterprise data centers, banks and financial infrastructure, large-scale PKI and certificate authority operations.
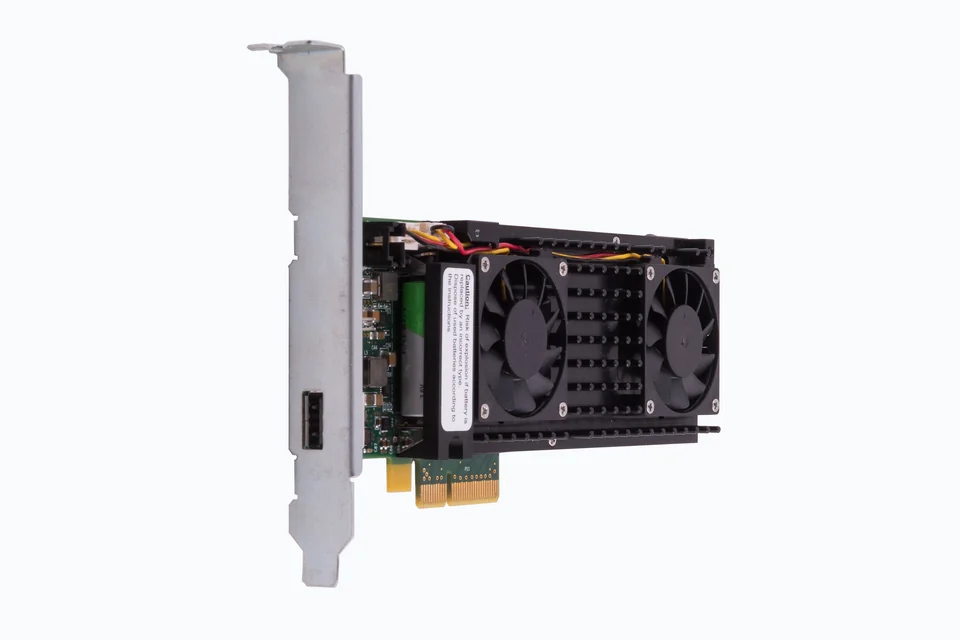
An HSM in card form - installs directly inside a server or appliance for dedicated, low-latency cryptographic acceleration without the network hop of a rack-mounted unit.
Because it lives inside the machine it protects, it fits naturally into embedded systems and appliances, or any application - code signing pipelines, database encryption, blockchain infrastructure - where a small footprint and direct hardware integration matter more than sharing one HSM across many servers.
Compact PCIe card, 18W max power draw
Up to 10,000 RSA / 20,000 ECC operations per second on the top performance tier
Three performance tiers (700 / 750 / 790), standard or multi-factor authentication models
FIPS 140-2/3 Level 3 validated, Common Criteria EAL4+ certified
Best for: OEM and embedded integration, code and document signing, blockchain and IoT security.
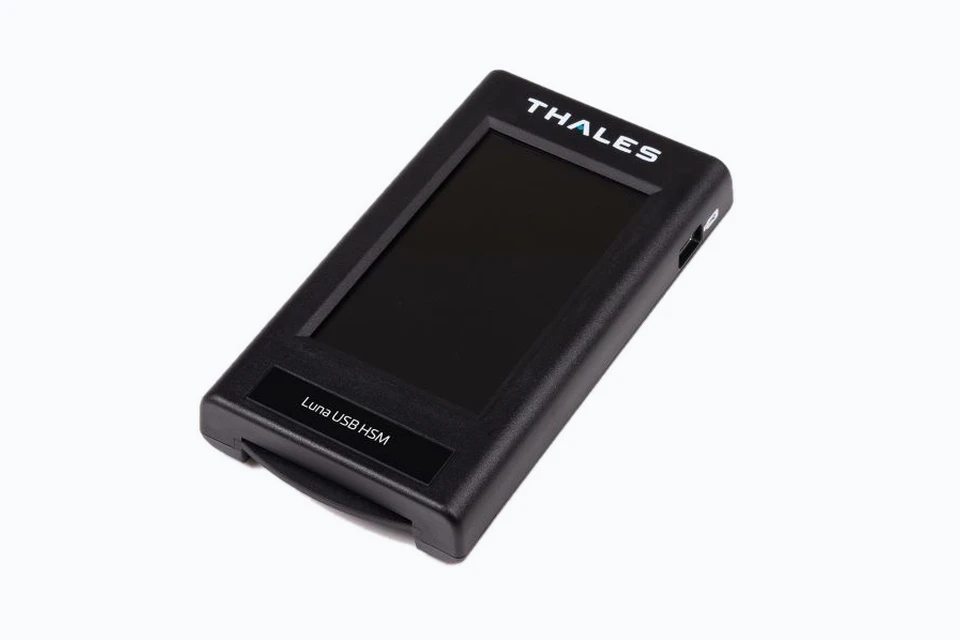
A portable HSM about the size of a small external drive - built for offline key storage rather than always-on production traffic.
This is the entry point into the Luna line: for protecting a root key that should almost never be online, for disaster-recovery key backups, or for teams that need certified key storage they can carry between secure sites without deploying a full rack appliance.
Portable USB 3.0 device, Windows and Linux support
FIPS 140-3 Level 3 certified
Multi-factor (Quorum M-of-N) authentication support
Signing performance from 8 to 340 transactions/second depending on key type
Best for: Root key and offline key protection, disaster recovery backup, portable certified key storage, BYOK scenarios.
HSM in the industry validated to FIPS 140-3 Level 3 - Luna Network and PCIe HSMs, NIST Certificate #4684
€22.1B
Thales Group's annual revenue - the scale and roadmap commitment behind the hardware protecting your keys
68+
countries with Thales operations, backing global 24/7 support and a decades-long product roadmap
FIPS 140-2 validated hardware was moved to NIST's Historical List in September 2026. If your key management infrastructure still relies on FIPS 140-2-only validated HSMs, now is the time to plan a migration to FIPS 140-3 Level 3 validated hardware like Luna.
Why Crypto-Agility Matters Now
Cryptographic keys and encrypted data captured today can be harvested by an attacker now and decrypted later once large-scale quantum computers become practical - a strategy known as "harvest now, decrypt later." For data, signatures, and credentials that need to stay valid or confidential for years, the migration to post-quantum algorithms needs to start well before quantum computers arrive, not after.
Luna HSMs are built for crypto-agility: the Luna 8 generation already supports NIST-standardized post-quantum algorithms (ML-KEM, ML-DSA) alongside RSA and ECC, and Thales participates directly in NIST's post-quantum cryptography standardization process. New algorithms can be introduced through firmware and configuration updates as standards evolve, rather than a forklift replacement of hardware already in production.
Frequently Asked Questions
General Purpose HSMs (Luna) are designed for broad cryptographic use cases - PKI, key management, code signing, application encryption. Payment HSMs (Thales payShield) are purpose-built for the payment card industry with specific command sets (Mark II, EMV) required by card schemes and payment processors.
Thales Luna HSMs are certified to FIPS 140-3 Level 3 (the highest level for network HSMs), Common Criteria EAL 4+, and meet requirements for use in NATO and government environments. They are the most widely government-certified HSMs available commercially.
Yes - Thales Luna HSMs integrate with AWS CloudHSM, Azure Dedicated HSM, and Google Cloud HSM services, as well as supporting Bring Your Own Key (BYOK) and Hold Your Own Key (HYOK) scenarios across all major cloud providers through the CipherTrust platform.
FIPS 140-3 is the current U.S. and Canadian government standard for validating cryptographic hardware, and Level 3 requires tamper-evident, tamper-resistant physical security in addition to strong cryptographic controls. Luna Network and PCIe HSMs were the first in the industry to achieve FIPS 140-3 Level 3 validation. FIPS 140-2 certificates were moved to NIST's Historical List in September 2026, so organizations still relying on FIPS 140-2-only hardware should plan a migration.
Yes - the Luna 8 generation supports NIST-standardized post-quantum algorithms (ML-KEM, ML-DSA) alongside traditional RSA and ECC, and Thales is an active participant in NIST's post-quantum cryptography standardization effort. Earlier Luna 7 deployments remain fully supported and can be planned for migration as part of a broader crypto-agility roadmap.
Get in touch
Request Thales Luna HSM Pricing
As a Thales reseller, Sersor handles procurement, deployment support, and compliance questions locally. Tell us about your use case and requirements - we will come back with a tailored proposal within one business day.
Thank you!
Your request has been submitted. We will be in touch within one business day.